Isolation Models for Ephemeral Environments: Full Copy vs Shared Cluster
The two ways ephemeral environments keep changes apart, a full copy of the stack or one shared cluster that deploys only the changed services, compared on cost, spin-up time and scale.
Every ephemeral environment has to keep one change from interfering with another, and there are two ways to do it. Infrastructure-level isolation duplicates the whole stack per environment. Shared-cluster isolation runs one set of stable services and deploys only the services a change touched, routing each environment’s requests to its own versions. This article compares the two. For what ephemeral environments are, the four ways to build them on Kubernetes and what each costs, start with the complete guide to ephemeral environments. For per-pull-request previews built on each model, see the complete guide to preview environments.
Why the isolation model matters
The isolation model decides what gets separated per environment and what gets shared. That one decision sets the cost of each environment, how long it takes to create, how many can exist at once, and how much work your services have to do to participate. Two teams can both say they run ephemeral environments and have bills that differ by an order of magnitude because of it. Coding agents raise the stakes, because they run many changes at once, which the complete guide to software factories covers.
Model 1: infrastructure-level isolation
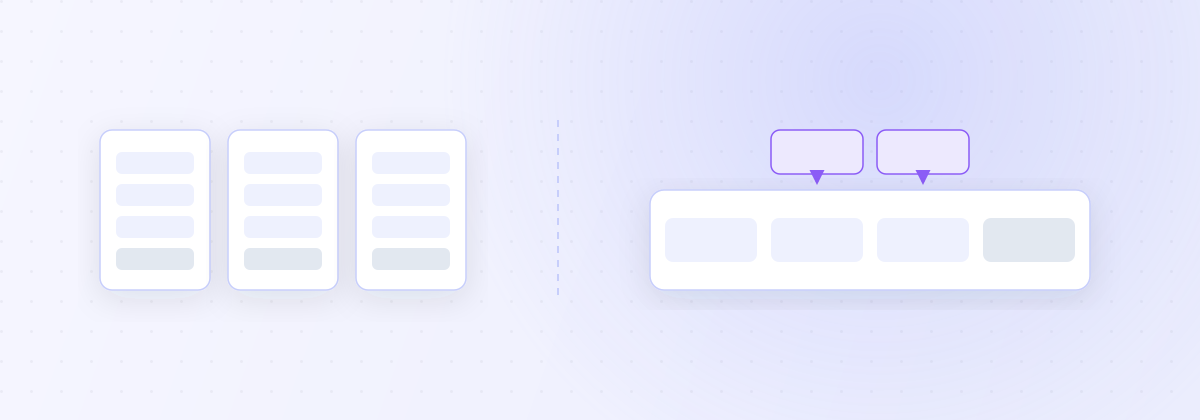
Every environment gets a complete copy of the system: every microservice, every dependency and a database instance of its own, in a separate namespace or cluster.
Strengths:
- Complete isolation, with nothing shared between environments
- A mental model anyone can follow: the environment is a copy of the system
Weaknesses:
- Cost scales with the number of services times the number of environments
- Slow to provision and tear down, because every service has to start
- Operationally heavy at scale, with dozens of copies of every database and cache to seed and keep current
Fits: Small systems, or teams with a hard tenancy requirement that can absorb the cost.
Model 2: shared-cluster isolation
One cluster runs one set of stable service versions. A developer, a CI job or an agent deploys only the services it is changing, and each environment gets a routing key. Requests carrying the key are routed, at every hop, to that environment’s version of a service when one exists and to the shared stable version when it does not.
Strengths:
- Very low infrastructure overhead, since each environment costs only the changed services
- Environments are created and destroyed in seconds
- Dozens or hundreds of isolated environments coexist on one cluster
- A natural fit for microservices and for many changes in flight at once
Weaknesses:
- Every service has to propagate the routing key on outgoing calls
- Routing needs a service mesh or a lightweight proxy in the request path
- Stateful side effects, such as schema changes and queue messages, need their own isolation plan
Fits: Engineering teams on microservices with many concurrent changes and tight feedback loops, including teams whose changes come from coding agents.
An analogy
Infrastructure-level isolation gives every developer their own house, with its own kitchen, plumbing and wiring. It is private, and it is expensive and slow to build.
Shared-cluster isolation is a co-working space with private meeting rooms. The building is shared, and each team gets a room of its own the moment it needs one.
How Signadot implements shared-cluster isolation
Signadot deploys only the modified services for each environment, as a Sandbox on a shared Kubernetes cluster, and routes tagged requests to them. The rest of the traffic flows through the stable shared versions, which keeps cost low and test fidelity high.
What that gives you:
- Environments that are ready in seconds
- Cloud spend that scales with changed services, not with the whole stack
- The same environment for CI pipelines, developers and coding agents
- Parallel testing at the scale of hundreds of environments on one cluster
Which model to choose
The isolation model decides whether ephemeral environments scale with your team or hit a wall.
- Infrastructure-level isolation is the easier one to reason about and becomes costly and slow past a handful of services.
- Shared-cluster isolation gives every developer, pull request or agent its own environment without duplicating the stack, at the price of header propagation and a plan for stateful dependencies.
As more teams move to microservices on Kubernetes and as coding agents multiply the number of changes in flight, the shared-cluster model is becoming the default way to build ephemeral environments that are fast, cheap and production-like.